

Quick answer
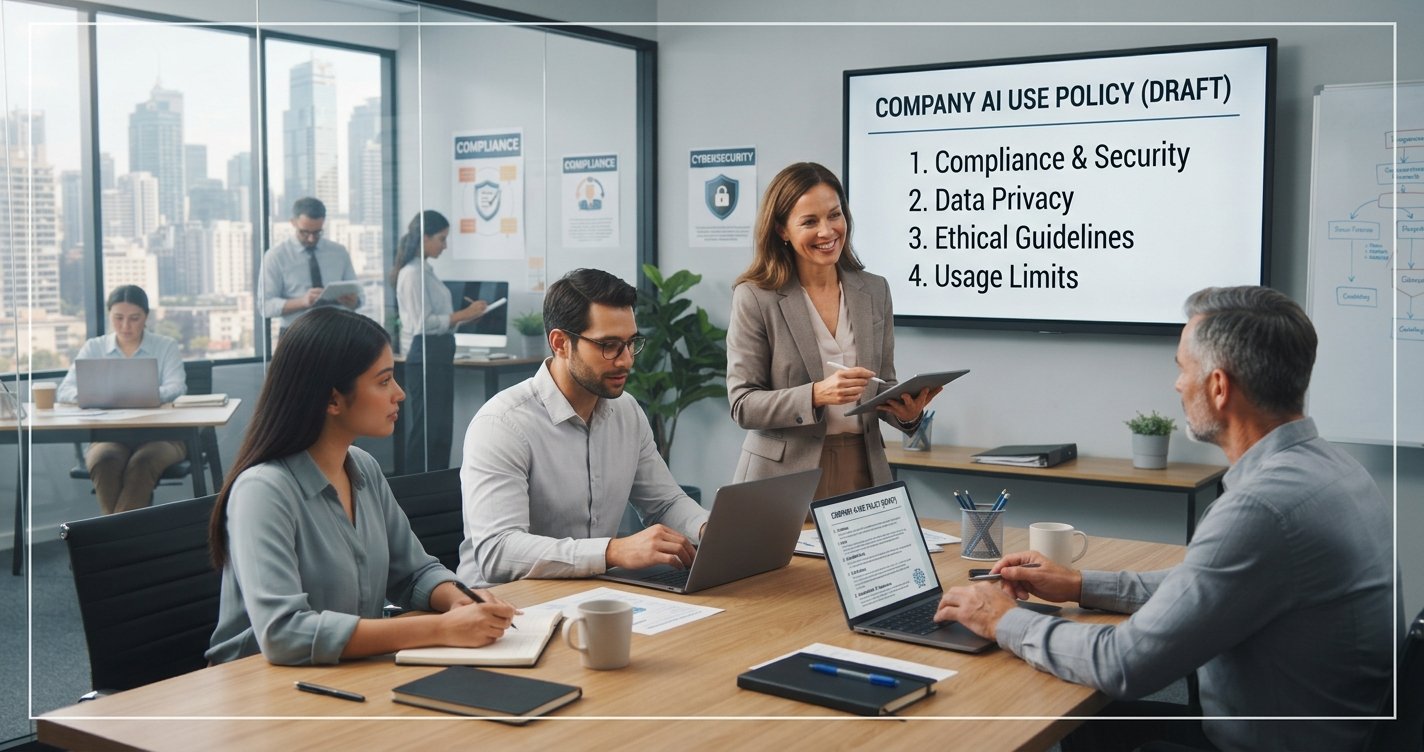
An AI use policy is a short document that tells your staff which AI tools they may use, what information they must never put into them, and who checks the results. You can write a workable one in an afternoon: list the tools, set data rules, require human review, name an owner, and train your team. A free template is included below.
Who this is for: owners and managers of businesses with 5 to 200 employees who know their staff already use ChatGPT or similar tools, but have no written rules yet.
Why your business needs an AI policy now
Your employees are almost certainly using AI already. They draft emails with it, summarise reports, write code and answer customers. Most do it with good intentions and no guidance.
That creates four real risks:
- Data leaks. A staff member pastes a client contract or salary sheet into a free AI tool. Depending on the tool’s settings, that text may be stored or used to train future models.
- Wrong answers sent as facts. AI tools sound confident even when they are wrong. An unchecked figure in a proposal or a made-up legal reference can cost you a client.
- Copyright and ownership questions. Content and images made with AI may raise questions about who owns them and whether they copy someone else’s work.
- Inconsistent quality. Without shared rules, one team uses AI carefully and another uses it carelessly, and customers notice the difference.
Banning AI does not solve this. Staff simply use it on their phones where you cannot see it. A clear policy lets your business get the time savings while controlling the risks.
How to write your AI use policy in 7 steps
Step 1: Find out what your staff already use
Before writing rules, ask. Send a short, no-blame survey: which AI tools do you use, for what tasks, and how often? You will likely be surprised. This tells you what the policy must cover and which tools are worth paying for.
Step 2: Decide which tools are approved
Sort tools into three groups:
- Approved: tools the company pays for or has checked, ideally business versions that do not use your data for training.
- Allowed with care: free tools that may be used only for non-sensitive tasks, such as brainstorming or rewording public text.
- Not allowed: tools with unclear data practices, or any tool for certain tasks.
Keep the list short and review it every three months, because AI tools change quickly.
Step 3: Set clear data rules
This is the most important part. Write down, in plain words, what must never go into an AI tool that is not company-approved. Typical examples are client names and contracts, personal data about customers or staff, financial records, passwords, and unreleased plans. A simple test helps staff decide: would I be comfortable if this text appeared in a newspaper? If not, it stays out.
Step 4: Require a human check
AI can draft; a person must approve. State that anything sent to a client, published, or used for a decision must be read and checked by a named employee. That person is responsible for the result, not the tool.
Step 5: Decide when to tell people AI was used
Set a rule for disclosure. Many businesses tell clients when AI produced a substantial part of a deliverable, and never present AI work as personal expert advice without review. Choose what fits your industry and your clients’ expectations.
Step 6: Name an owner
One person should own the policy: answering questions, approving new tools and updating the rules. In a small company this may be the owner or operations manager. Without an owner, the policy is forgotten within a month.
Step 7: Train your team and review regularly
A policy nobody reads protects nothing. Hold a 30-minute session, walk through real examples, and ask each employee to sign that they have read it. Put a review date on the document and update it at least twice a year.
Free AI use policy template
Copy this template, replace the words in [brackets], and remove anything that does not apply to your business. It is a starting point, not legal advice; for regulated industries such as finance or healthcare, have a lawyer review your final version.
[COMPANY NAME] AI USE POLICY
Version 1.0 | Effective date: [DATE] | Policy owner: [NAME, ROLE]
Next review: [DATE]

1. PURPOSE
This policy explains how employees may use artificial intelligence (AI) tools at [Company Name]. Our goal is to benefit from AI while protecting our clients, our staff and our reputation.

2. WHO THIS APPLIES TO
All employees, contractors and interns who use AI tools for any work task, on company or personal devices.

3. APPROVED TOOLS
- Approved for all work: [e.g. business version of tool X]
- Allowed for non-sensitive tasks only: [e.g. free versions of public chatbots]
- Not allowed: any tool not listed above, unless approved in writing by the policy owner.

4. INFORMATION YOU MUST NEVER ENTER INTO A NON-APPROVED AI TOOL
- Client names, contracts or project details
- Personal information about customers or employees
- Financial records, pricing or payroll data
- Passwords, access codes or system details
- Unpublished plans, products or strategies
If in doubt, leave it out and ask the policy owner.

5. CHECKING AI OUTPUT
AI output must be reviewed by a responsible employee before it is sent to a client, published, or used to make a decision. The reviewing employee is accountable for its accuracy.

6. DISCLOSURE
[Choose one] We tell clients when AI tools produced a substantial part of a deliverable. / We do not require disclosure for internal drafts, but final client work must always be human-reviewed.

7. INTELLECTUAL PROPERTY
Do not use AI to copy or closely imitate other people's copyrighted work, logos or brands. Check AI-generated images and text before commercial use.

8. NEW TOOLS AND QUESTIONS
Requests to use a new AI tool go to [Policy Owner]. Questions about this policy go to [Email].

9. BREACHES
If sensitive information is entered into an AI tool by mistake, report it to [Policy Owner] the same day. Reporting quickly is always better than hiding a mistake. Deliberate breaches may lead to disciplinary action.

10. ACKNOWLEDGEMENT
I have read and understood this policy.
Name: ________  Signature: ________  Date: ________
My view: rules work when people understand why
A policy alone does not protect a business; the ecosystem around it does. Over the years I have seen that rules hold only when three things are present: structure (a clear owner), feedback (people report mistakes without fear) and adaptation (rules change as the tools change). An AI policy is one part of that ecosystem, not a substitute for it.
In my experience, the organisations that handle sensitive information well are not the ones with the longest rulebooks. They are the ones where every person understands what is at stake and knows exactly whom to ask. An AI policy should work the same way: short enough to remember, clear enough to follow under pressure, and owned by someone people can reach.
Common mistakes to avoid
- Copying a big company’s policy. A 20-page corporate document will not be read in a 15-person firm. Keep yours to two pages.
- Banning AI outright. Staff will use it anyway, just out of sight.
- Writing it once and forgetting it. Tools change every few months; set a review date.
- No owner. If nobody is responsible, nobody updates it or answers questions.
- Punishing honest mistakes. If staff fear punishment, they hide data leaks instead of reporting them.
Next steps
- Copy the template above and fill in the brackets.
- Send the short staff survey from Step 1 this week.
- Book a 30-minute team session to walk through the final policy.
Have a question about writing your own AI policy? Leave it in the comments below and I will answer it.
About the author
Dr. Atique Ur Rehman is the founder and CEO of Digital and AI Solutions (DAIS) and a retired military officer with UN peacekeeping experience. He is the author of more than 20 books on geopolitics, governance and AI, including The Sovereign Inforg, Future of Humanity and New Information Order. He holds a PhD in International Relations and writes for The Nation and Daily Times. See his books
About the Author